EDIT: most recent observation
After working with Blender for a while, it seems some addons still don’t work. I can’t exactly understand what happens but every time I use one operator in Blender, new files of this form are generated:
C_python.exe_FD243E4545B32FF54FD7610C4E7314BB73AA5B62.py
These files contain just this line of Python code:
from multiprocessing.spawn import spawn_main; spawn_main(parent_pid=13604, pipe_handle=4252)
where pipe_handle is different. The operator in Blender is blocked with the error PermissionDenied. Marking these files as Trusted didn’t work, I assume because these files are created on demand (?).
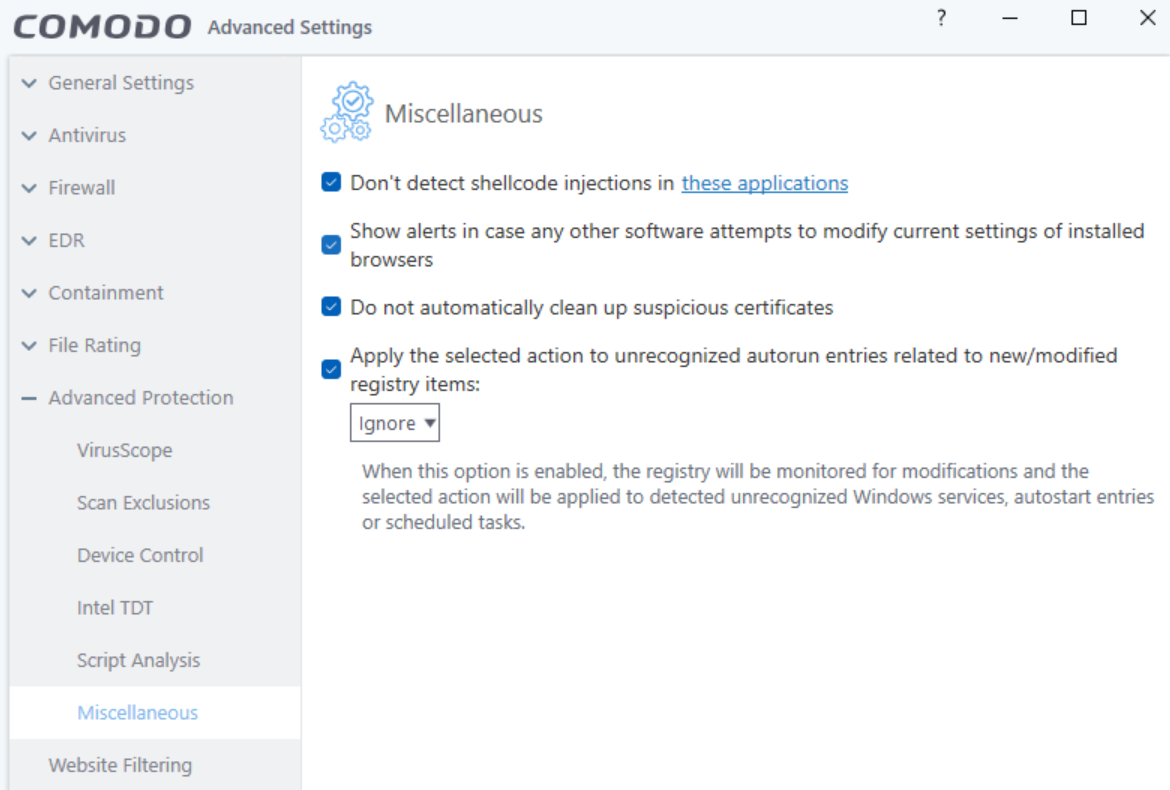
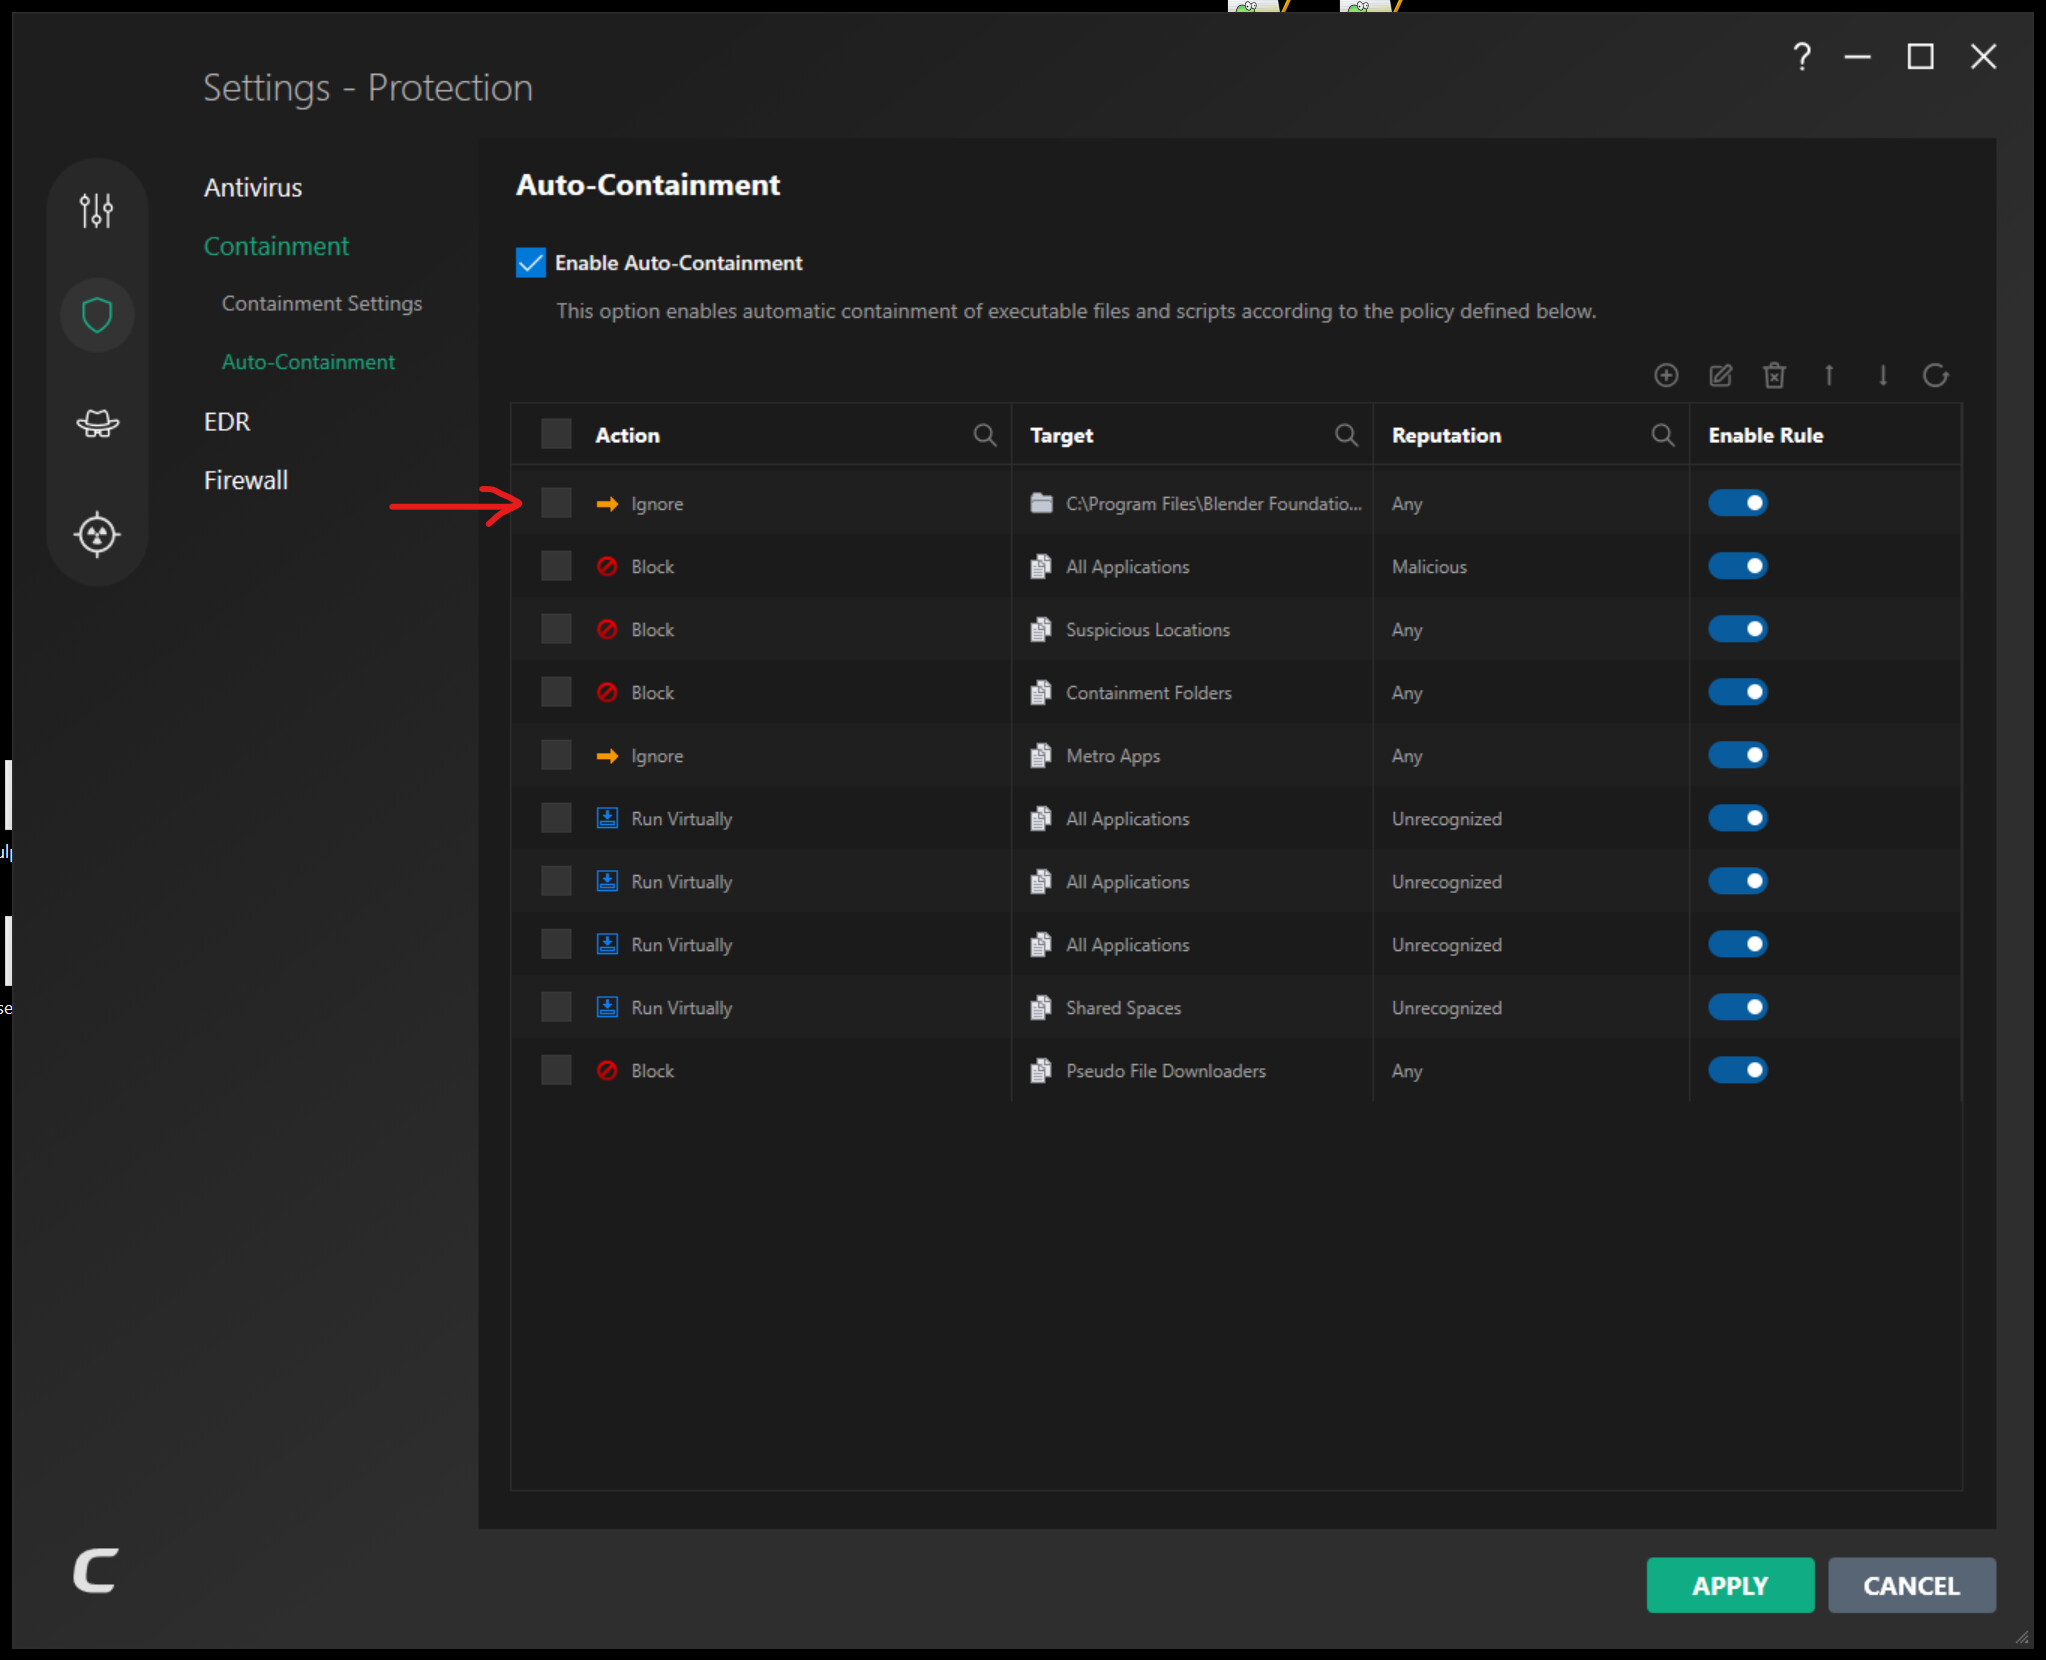
Since the previous solution had not worked, I simply created one exception for blender.exe in Auto-Containment, which stopped CIS from blocking addons.
I can’t say whether this is a proper solution to solve my problem.
Original post
I have a problem with Blender + CIS 2027.
Blender is a vastly modular program whose addons are coded in Python including code for running functions, and generating custom panels and other elements of UI.
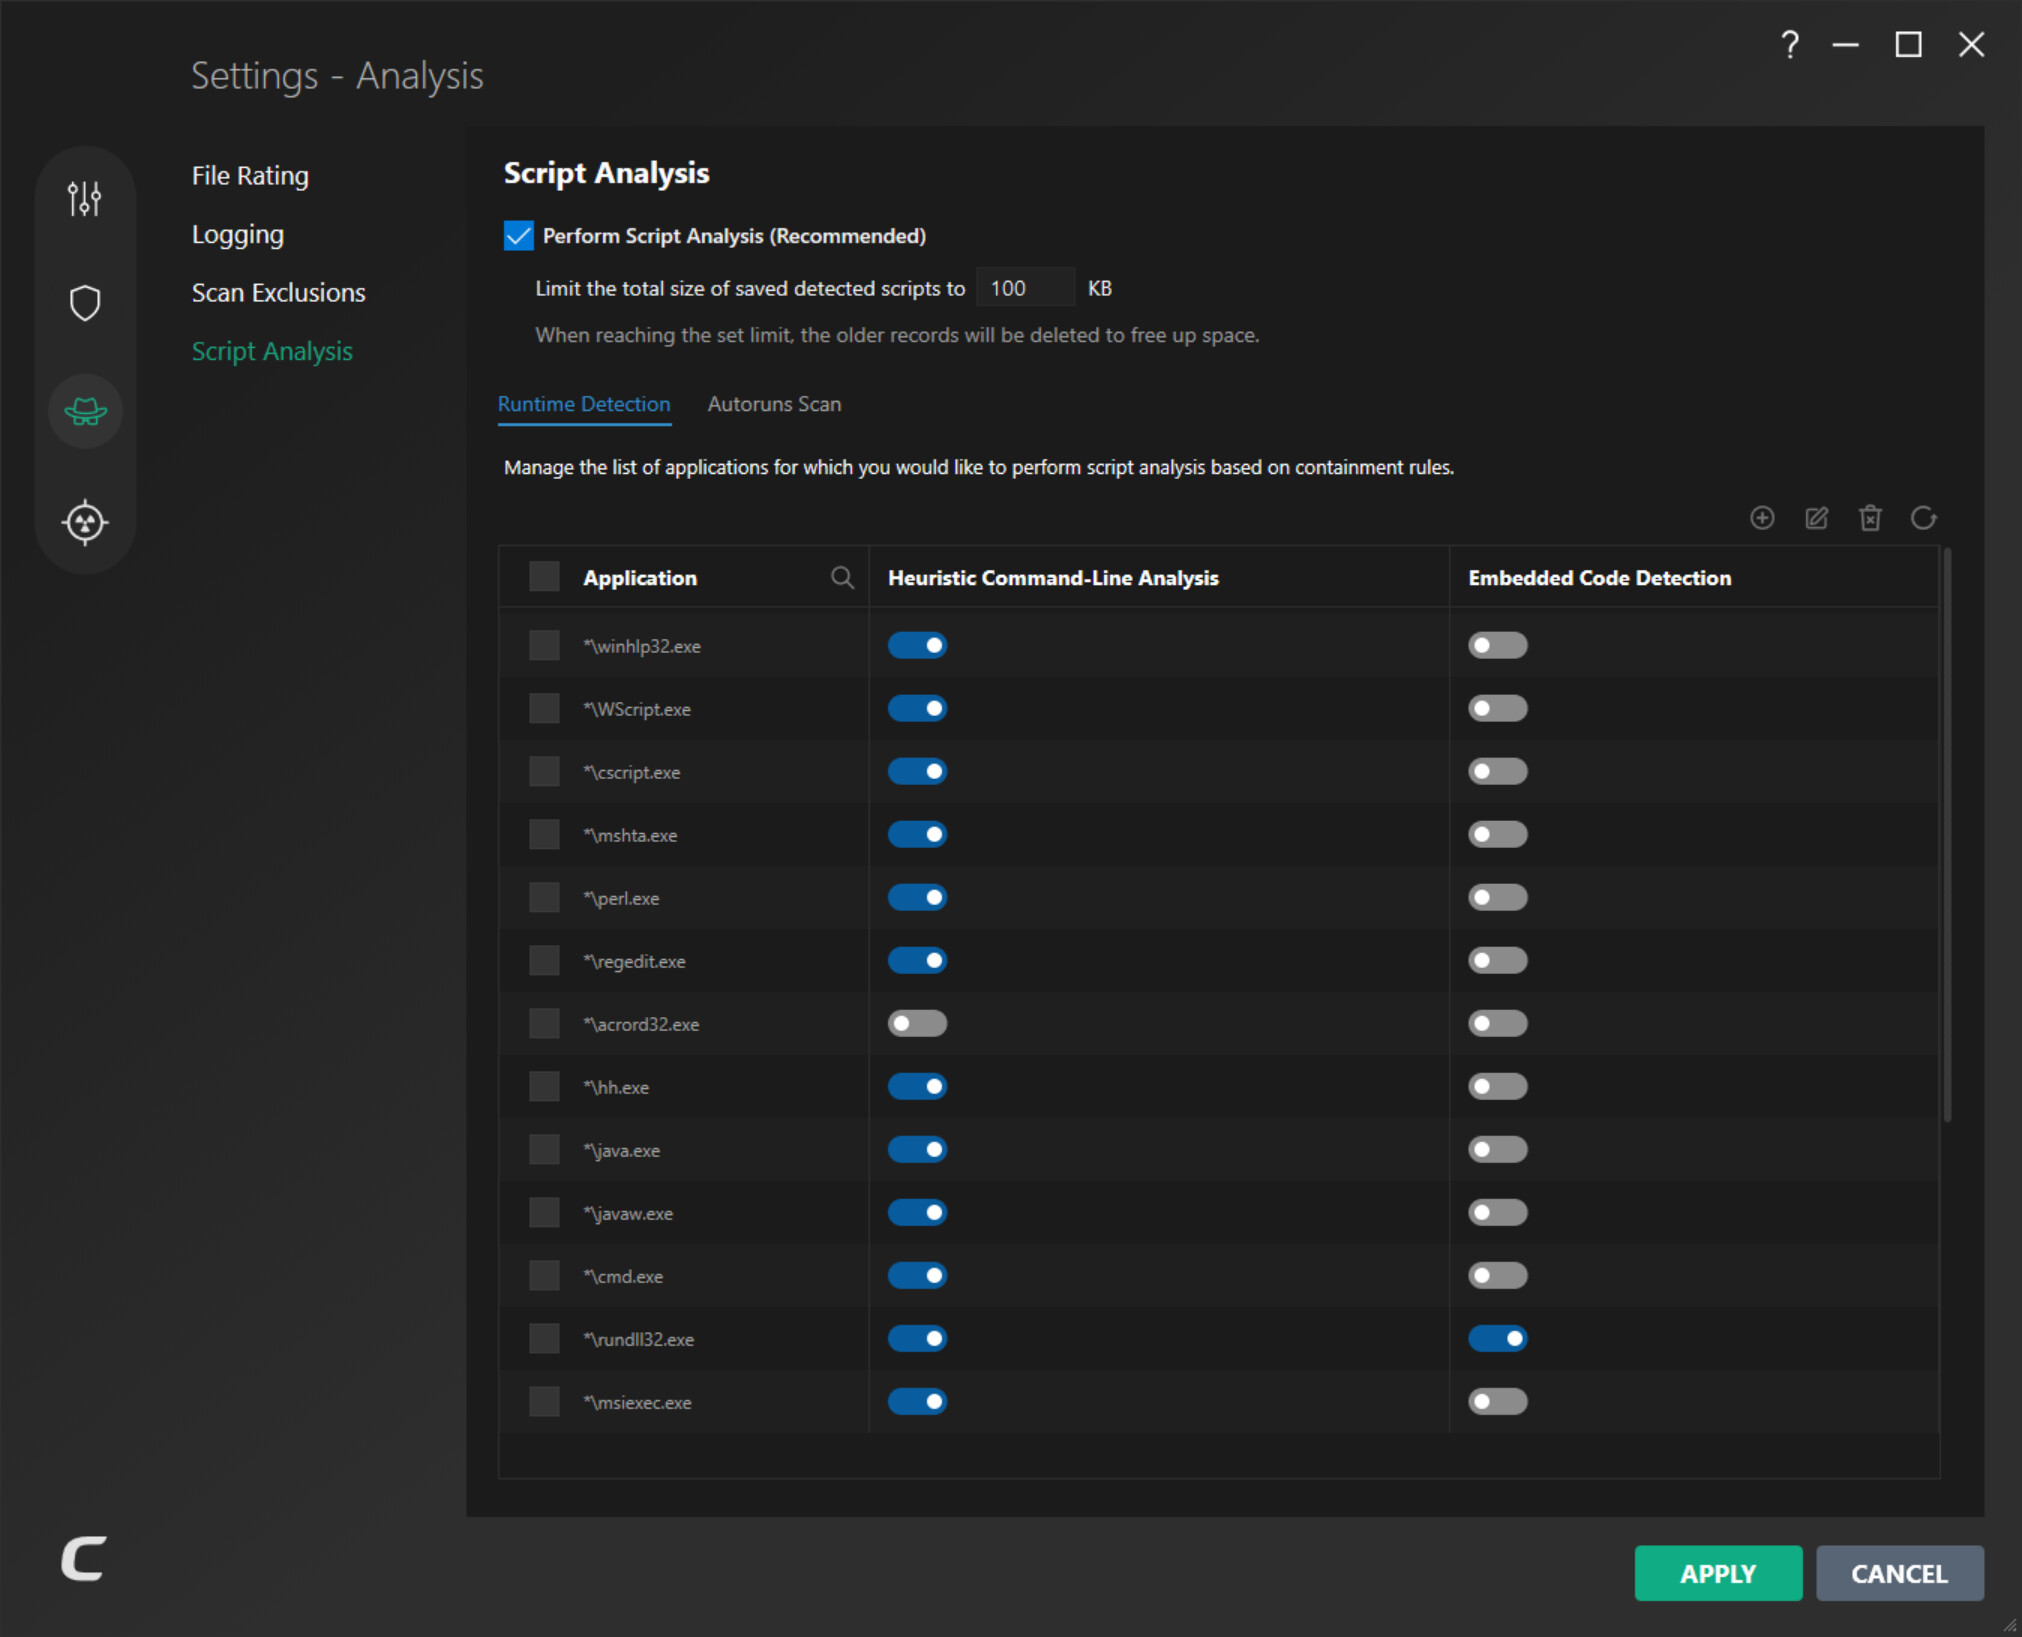
As I understand, Python may execute harmful code and CIS run such scripts in contained environment, or simply virtually. I also understand, this is controlled by Settings → Analysis → Script Analysis (at least in the new CIS 2027). Without handling this, Blender addons simply do not function because scripts need to be executed correctly.
I have tried two approaches and both work. However, I’d like to ask if these approaches are OK, especially the second one or am I putting myself into troubles?
Disabling Python
First, I could simply disable both python.exe and pythonw.exe in Settings → Analysis → Script Analysis. This indeed sorts out the problem because Python CIS no longer handles scripts. Personally, I don’t like it.
Exception in Containment section
I realised CIS run each scripts virtually. Hence, in Containment Settings I thought I could add a folder containing addons to the list of Do not virtualise access to the specified files/folders.
The latter seems better because I can control or narrow folders that are ignored by CIS. Whereas there might still be a script somewhere in the system which can cause damage. The latter approach would also be great because I make addons by myself and would add my personal folder to exception and would not have to clear CIS every time I make changes.
Is there any better, or perhaps more secure way of doing this?
Thanks