Hello yigido,
Thank you four submissions, we’ll check them.
Best regards,
FlorinG
Hello yigido,
Thank you four submissions, we’ll check them.
Best regards,
FlorinG
Trusted Malware
SHA-1 : 74ce4a67687b19d2bea5e4cf7ece3fa222307c2d
File persist in File Intelligence!
Trusted Potential Unwanted App - PUA Hacktool
SHA-1 : 9d6d0fea98e4d6ba614d9c1bdc24d2e83451b228
Hi,
Thank you for your submission.
We’ll check these.
Best regards
Qiuhui.■■■■
Truested Malware
SHA1: cccfe140340370a7b8ccf70e76c0284203e26322
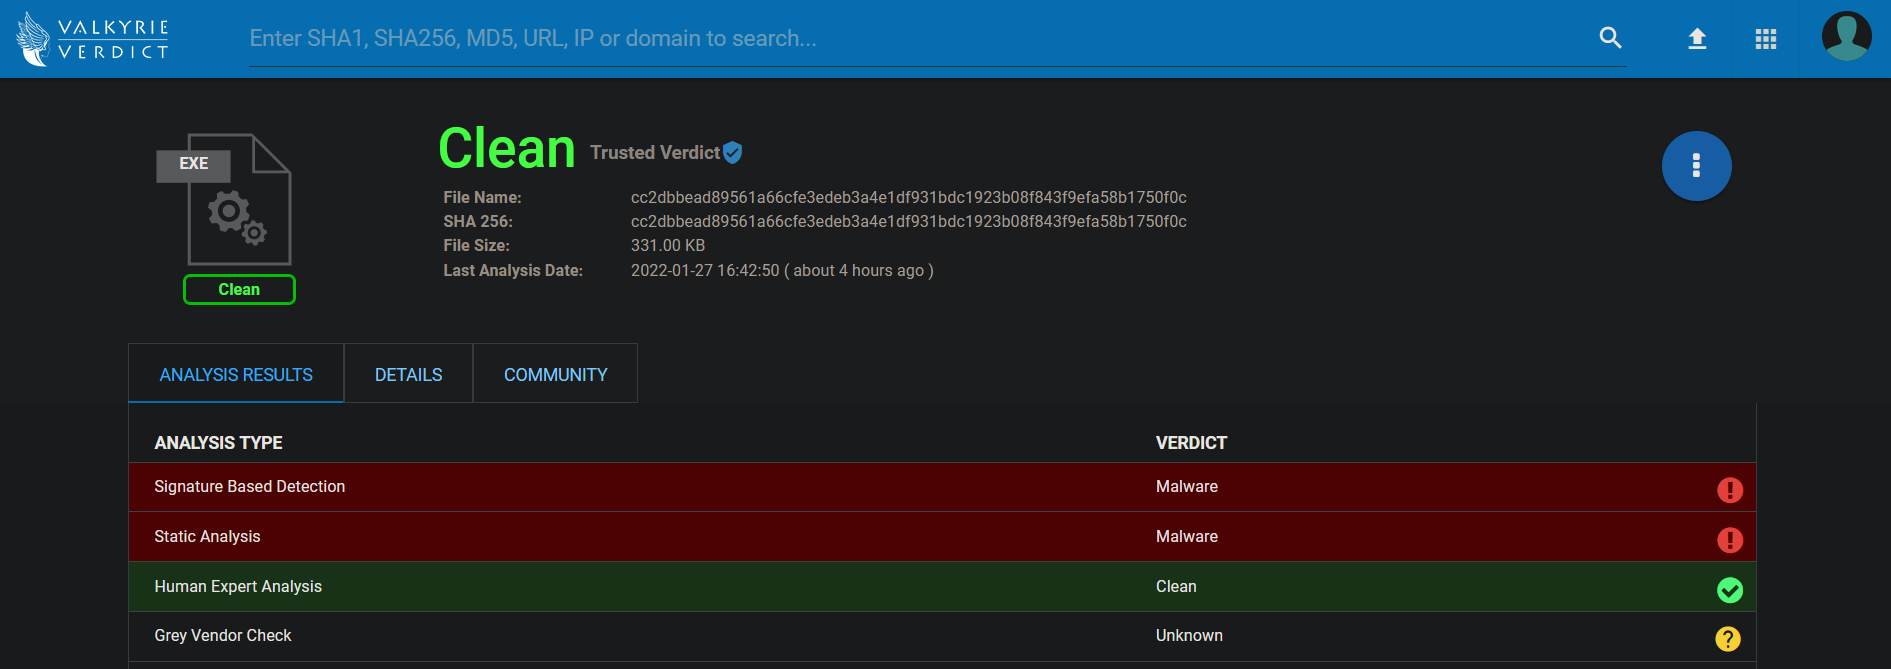
“Human Expert Analysis” says it is safe! How did this happen?
Hello yigido,
Thank you for sharing this, we’ll check this.
Best regards,
FlorinG
Hi FlorinG,
Please remove “InstallShield Software Corporation” vendor from Trusted Vendor List (TVL)
One example is enough for deleting it from “Trusted”
Please see screenshot
Please check it.
Thanks,
yigido
Hi yigido,
The TVL layer does not work as you might think.
Thanks,
Bogdan
Hi Bogdan,
Please see the attached screenshot.
It shows the trusted PUA submission above. Same hash (SHA1 : cccfe140340370a7b8ccf70e76c0284203e26322 )
Thanks,
For the submitted file - the cert is not valid. As per your screenshot, it just says signed (signature not validated, CIS would validate status on encounter and check against tvl only if valid) and the company stated is taken from file version, not from cert name (it does not state that the certificate name is the company name which distributes the file , the company name is taken from file version, these are totally 2 different things). Can you please specify the comodo product and version you are using (from screenshot)?
Attached
Why you guys add Potential Unwanted Apps to whitelist? Joke samples shouldn’t be whitelisted :-TD
In my opinion, some files should stay in gray area. It may be not bad but not safe either. Please remove the clean verdict of these samples.
Trusted Joke Malwares - PUA
Hello yigido,
Thank you for reporting this. We’ll check these.
Best regards,
FlorinG
CryptoMiner Avira :o
SHA1 : 02fcdb0689dc1a0c22fdef35f3065bfe0da8ba31
Hi,
Thank you for your submission, we’ll check it.
Kind Regards,
Erik M.
Trusted Malware
SHA1 : 0b2c3ac006c0321b51bc92dd3f3cdef0ffea3381
Hi,
Thank you for your submission, we’ll check it.
Hello meldan,
The file is malicious for signatures, detected on VirusTotal but verdict is still clean on Verdict Valkyrie Service.
File is not detected by CIS.
What can we do this ?
Thanks for marking it as malicious.
Hello yigido,
Thank you for sharing this, it should be fixed now.
Best regards,
FlorinG